
By Fábio Rego, Business Solutions and Compliance Lead, Ascertia
Why scalable digital trust will require new thinking around infrastructure, certification, and auditability?
The Challenge:
A New Scale of Digital Trust Qualified Trust Service Providers (QTSPs) are entering a period of unprecedented growth. Regulatory initiatives such as eIDAS 2.0 and the rollout of the European Digital Identity (EUDI) Wallet are expanding both the scope and scale of digital trust services across Europe.
Under eIDAS 2.0, new qualified services are being introduced, including:
- Electronic archiving
- Electronic ledgers
- Qualified electronic attestations of attributes (QEAAs)
- Remote management of qualified signature and seal creation devices.
At the same time, the EUDI Wallet is expected to drive significant demand for the issuance and management of digital credentials and QEAAs across Member States.
These attestations will enable users to securely prove attributes such as qualifications, professional status, licences, and other verified information directly from their digital wallets, creating substantial new volume requirements for QTSPs.
Alongside these regulatory developments, organisations are increasingly adopting remote signing and digital identity services as part of broader digital transformation initiatives. As a result, QTSPs are being asked to support higher transaction volumes, greater service availability, and faster deployment cycles than ever before.
Many existing trust service platforms were designed around dedicated physical infrastructure and predictable workloads. The question facing the industry is whether these traditional architectures can continue to scale efficiently or whether a new approach is needed to support the next generation of digital trust services.
What Does Cloud Native Really Mean?
When discussing the future of QTSP infrastructure, it is important to distinguish between simply moving existing systems to the cloud and adopting a truly cloud native approach.
Running a trust service platform on virtual machines in a public cloud is not, by itself, cloud native. Rather, cloud native architectures are designed from the outset to take advantage of capabilities such as:
- Containerisation
- Automation
- Elastic scaling
- Built in resilience.
For QTSPs, this means services can be deployed, updated, and scaled independently according to demand. High-volume components, such as validation or status services, can expand automatically during periods of peak usage, while other services continue operating unchanged. Infrastructure can be managed through automated deployment pipelines rather than manual server configuration, improving consistency and reducing operational overhead.
The result is an architecture that is inherently more scalable, resilient, and adaptable. As demand for digital trust services grows, these characteristics are becoming increasingly important.
The Certification Challenge
The case for cloud native architectures is compelling, but qualified trust services face a challenge that many other industries do not: certification requirements are tied to specific hardware and security boundaries.
At the heart of every qualified trust service are cryptographic components that protect signing keys and ensure the integrity of trust operations. These include Hardware Security Modules (HSMs) and, in the case of remote qualified signatures, Remote Qualified Signature Creation Devices (RQSCDs). These components provide the certified security controls required under eIDAS and related standards.
Unlike application workloads, these systems cannot simply be treated as ephemeral cloud resources. Their certifications are linked to defined hardware, software and operational configurations, creating boundaries that must be maintained throughout the lifecycle of the service.
QTSPs must therefore balance two competing objectives: the flexibility and scalability offered by cloud native infrastructure, and the need to preserve certified trust anchors that underpin the legal validity of qualified services.
This does not mean cloud native architectures are incompatible with qualified trust services. Rather, any transition must carefully consider where certified components remain anchored and how those certification boundaries are maintained, monitored, and audited.
A Hybrid Future for Qualified Trust Services
For most QTSPs, the future is unlikely to be a choice between traditional infrastructure and a fully cloud native model. Instead, the industry is more likely to adopt hybrid architectures that combine the strengths of both approaches.
In such a model, certified trust anchors, including HSMs, RQSCDs and other critical security components, would continue to operate within tightly controlled and audited environments. These elements provide the foundation of trust and legal assurance on which qualified services depend and will remain subject to rigorous certification and conformity assessment requirements.
Around these certified components, however, cloud native approaches can be applied to a much broader range of supporting services. Identity workflows, validation services, orchestration layers, user-facing applications, monitoring platforms, and operational tooling can all benefit from greater automation, elasticity, and resilience. Services can be scaled independently, deployed more rapidly, and operated more efficiently while maintaining the integrity of the underlying trust framework.
This approach recognises that cloud native is not an all-or-nothing proposition. The objective is not to replace certified trust anchors, but to make the surrounding ecosystem more agile and scalable in response to growing demand.
Achieving this vision will require continued collaboration across the trust services community. QTSPs, conformity assessment bodies, auditors, technology providers, and regulators will need to work together to develop common reference architectures, consistent audit methodologies, and practical guidance for cloud native deployments.
As digital trust services continue to expand through eIDAS 2.0 and the EUDI Wallet ecosystem, the question is no longer whether the industry can benefit from cloud native approaches. The challenge is determining how they can be adopted while preserving the assurance, security, and legal certainty on which qualified trust services are built.
Conclusion
Qualified trust services are unlikely to become fully cloud native in the near term, but neither will they likely remain wholly dependent on traditional infrastructure. A hybrid model that combines certified trust anchors with cloud native services offers the most practical path forward.
Realizing that visions will require common reference architectures, consistent audit methodologies, and evolving standards that enable greater scalability and innovation without compromising trust. The opportunity now is for the industry to define how cloud native principles can be applied in a way that strengthens, rather than challenges, the foundations of digital trust.
By Edmar Araujo, Executive Director at the Brazilian Association for Digital Certification (ANCD)
Brazil is undergoing a significant transformation in its digital trust infrastructure. After more than two decades of consolidating the Brazilian Public Key Infrastructure (ICP-Brasil), the country is moving toward a more accessible, interoperable, and user-centric model while maintaining the high standards of security and legal validity that characterize qualified trust services.
With over two decades of experience in public key infrastructure, Brazil has established one of the world’s largest digital certification ecosystems. Since the creation of ICP-Brasil in 2001, the country has developed a governance model capable of ensuring legal validity, authenticity, integrity, and non-repudiation in electronic transactions carried out by citizens, businesses, and public institutions.
One of the key developments in this direction is the expansion of the Electronic Registration Authority (e-RA), a model designed for the remote issuance of digital certificates to natural persons. The Electronic Registration Authority aims to expand access to qualified trust services through fully digital processes while maintaining the security requirements established by ICP-Brasil. Under this model, subscriber identity verification is performed using robust mechanisms such as biometric verification, liveness detection, and cross-checking against official and authoritative data sources. Certificates issued under this model are stored in the cloud, enabling their secure use across multiple devices and digital environments.
Although remote issuance represents a recent step toward democratizing access to digital certification, cloud-based certificates have been part of the Brazilian landscape since 2018. Their adoption has been enabled by Qualified Trust Service Providers (QTSPs), which offer solutions that ensure the secure custody of cryptographic keys and support the execution of qualified electronic signatures through mobile devices and cloud-based applications.
The combination of cloud-based certificates and the Electronic Registration Authority creates the conditions necessary to expand the reach of qualified trust services, reducing operational barriers and bringing digital certification closer to citizens’ daily lives.
This movement is particularly relevant in a context of increasing digitalization of public and private services, where digital identity, secure authentication, and interoperability are becoming essential elements for building trust in electronic environments.
Recent developments in Brazil’s trust infrastructure were widely discussed during CertForum ID 2026, one of the country’s longest-running events dedicated to digital certification, electronic signatures, and digital identity. Held annually since 2003, the event brings together representatives from government, industry, academia, and international organizations to discuss the challenges and opportunities associated with digital transformation.
The 2026 edition reinforced the importance of qualified trust services as essential tools for modernizing public administration, combating fraud, and expanding digital citizenship.
Discussions covered topics such as remote certificate issuance, cloud signatures, electronic seals, verifiable credentials, artificial intelligence, interoperability, and the impact of emerging technologies on traditional trust models. One of the central themes was the need to balance security, usability, and digital inclusion, ensuring that robust technological solutions are also accessible and intuitive for users.
The event featured Esther Dweck, Brazil’s Minister of Management and Innovation in Public Services, whose participation reinforced the importance of trust infrastructure to the country’s digital transformation strategy and the expansion of digital public services.
Another significant development for the Brazilian ecosystem was the establishment of the Digital Partnership between Brazil and the European Union. Although the agreement does not establish specific technical standards for electronic signatures or trust services, it creates a favorable environment for dialogue and cooperation on topics such as digital identity, data governance, interoperability, cybersecurity, and digital transformation. The initiative opens new opportunities for the exchange of experiences among governments, industry associations, and technology providers while strengthening discussions on mechanisms that enable secure cross-border digital interactions.
As digital ecosystems become increasingly interconnected, building interoperable trust frameworks is becoming a fundamental requirement for economic development and the delivery of cross-border digital services. Brazil’s experience demonstrates that it is possible to expand access to qualified trust services by combining technological innovation, legal certainty, and institutional cooperation.
More than simply modernizing processes, the current challenge is to build a trust infrastructure capable of supporting the next generation of digital interactions among citizens, businesses, and governments.
by Markus Vesely, CEO, A-Trust GmbH
For A-Trust, as a qualified trust service provider operating within the eIDAS regulatory framework, participating in CSC Trust Without Borders 2026 was a natural decision. With more than 25 years of experience in digital trust services, participating in the Summit aligned with our long-standing engagement in the field in shaping how digital trust evolves both in Austria and internationally. Events like this bring together the key people shaping the future of digital identity and electronic signatures. The direct exchange with other industry participants, whether during panels, presentations, or informal conversations on the sidelines, is hard to replicate through any other form of communication. What makes CSC Trust Without Borders Summit particularly valuable is the international dimension of that exchange: connecting with experts, innovators, and decision-makers from across the globe gives us perspectives that go far beyond what any regional event could offer. Hearing how different countries and markets approach the challenges of digital trust, what solutions they are developing, what regulatory paths they are taking, and what lessons they have already learned is enormously enriching. It challenges our assumptions, sparks new ideas, and reminds us that the community we are all building together is truly a worldwide one. Networking and knowledge sharing at this international level are a core part of our strategic work, and sponsoring Trust Without Borders 2026 was our way of actively contributing to that conversation and to the broader community driving digital trust forward.
What was the biggest insight you gained from the event?
A-Trust was represented at CSC Trust Without Borders Summit 2026 by our CEO, Markus Vesely, who also took the stage as a speaker at the event. He shared insights into Austria’s approach to the EUDI Wallet and brought the Austrian perspective on digital identity and interoperability to an international audience. Being present in person and engaging directly with experts and decision-makers from around the world gave us a first-hand sense of how Colombia and other Latin American countries are approaching areas such as digital identity and electronic trust services, and how strong the interest in the European EUDI Wallet already is in this part of the world. This significantly broadened our view of the global dynamics shaping this landscape. One of the most remarkable experiences was a small-group technical visit to Quipu, Colombia’s first quantum computer, at the Universidad de los Andes in Bogotá. Quantum computers differ fundamentally from classical machines: instead of relying solely on bits, they use qubits, which can represent multiple states at the same time through a phenomenon called superposition. Together with quantum entanglement, this principle is the foundation for technologies that may, in the future, unlock significant potential in fields such as cryptography, materials science, and chemical simulation – areas of long-term relevance to our work on digital trust services. Seeing this technology was a powerful reminder of how important it is to track emerging developments early and think through their strategic implications.
What challenge should the digital trust ecosystem address next?
The many on-site presentations and discussions made it clear where the industry stands today and where it is heading. A central theme running through the event was the question of viable business models for the EUDI Wallet and the Business Wallet. What business models are sustainable in the long run? Who takes on which role within the ecosystem? These questions remain open, and that is precisely the next major challenge for the sector. What is needed is not only technical interoperability, but also economic sustainability and clear governance structures that enable trust across borders.
What are your organization’s priorities for the next 12 months?
For A-Trust, the next twelve months will be defined by actively co-shaping the EUDI Wallet ecosystem. The insights from Bogotá, like technological trends, international perspectives, and new ideas for potential business models, feed directly into our strategic planning. We will continue contributing to the development of digital trust solutions while keeping a close eye on the evolving regulatory landscape. At the same time, we aim to strengthen our role as a reliable partner for organizations looking to integrate qualified electronic signatures, qualified seals, and digital identity solutions into their processes.
How can industry collaboration help advance digital trust globally?
CSC Trust Without Borders Summit 2026 was an impressive demonstration of what becomes possible when players from different regions and backgrounds come together. Digital trust is not a national issue; it is a global infrastructure challenge. For us, collaboration means developing shared standards, openly exchanging experiences, and learning from one another. Only through this kind of open, cross-border exchange can a digital trust ecosystem emerge that is truly built to last.
By Enrique Enciso, Regional Sales Manager — Latin America, GMO GlobalSign
I have been working in technology sales across Latin America for nearly two decades. In that time, I have sat across from countless CISOs, IT directors, and IT teams in markets stretching from Mexico to the Southern Cone, and I have watched digital security move from a line item that required justification to a strategic imperative for all organizations. So, when I say that something felt different at the CSC Trust Without Borders Summit 2026 in Bogotá, I mean it. The conversations at the CSC Trust Without Borders Summit 2026 reflected a community that understands the stakes and is actively working to meet them.
I left Bogotá with pages of notes, a stronger network, and a renewed sense of why this work matters.
Regulation and Digital Signatures:
The Challenge I See Every Day. From the discussions around cross-border interoperability and regulatory alignment, digital identity wallets and portable trust, pressure from the growing reliance on AI, to preparing for Post-Quantum Encryption, the event truly captured some of the digital identity industry’s pressing issues. Every market I cover — Mexico, Colombia, Chile, Argentina, and the others — is at a different stage of developing or updating its legal framework for electronic and digital signatures. What is legally valid in one country may not be recognized in another. What satisfies compliance requirements today may need to be revisited when a new decree or standard comes into force next year. The digital trust landscape is genuinely complex, and it is exactly the kind of complexity that does not get resolved by any single vendor or any single government. It requires the kind of multi-stakeholder conversations that the CSC Trust Without Borders Summit made possible. Sitting in those sessions, I found myself nodding along, knowing a room full of people who share the same challenges and are serious about solving them together.
One theme that kept surfacing was how organizations are struggling to build cross-border workflows on top of signature frameworks that were designed with only domestic use in mind. That is a problem I hear from theindustry constantly, and it was energizing to see it treated as a shared responsibility rather than an individual compliance headache. Bogotá was the ideal site for these conversations. Colombia has continued to develop its digital identity and electronic signature framework, and that context gave the discussions a particular edge and relevance.
Why Showing Up Maters Looking Ahead
GlobalSign participated in the Cloud Signature Consortium’s Trust Without Borders Summit 2026 as a supporting sponsor, alongside regional partner GSE and SSL.com. It was an important opportunity to be part of the ecosystem, contributing to the momentum. As a long-established Certificate Authority (we will celebrate our 30th year in business later this year), GlobalSign has a long-standing interest in the development of digital trust frameworks, not just commercially, but technically and structurally. The standards discussed in forums such as the CSC Trust Without Borders Summit will influence future digital trust ecosystems.
Having worked across Latin America for nearly two decades, I have seen the importance of maintaining dialogue through events such as this.
Looking Ahead
The road ahead for digital trust in Latin America is not without its challenges. The discussions in Bogotá demonstrated the expertise, collaboration and commitment that exist across the digital trust community. As more markets move toward binding frameworks for digital signatures and identity verification, the decisions made in forums like this one will matter enormously.
As global trade evolves, one thing is becoming increasingly clear. Trade agreements alone are not enough. Digital trust must follow.
This was the focus of the latest Member Insights session hosted by the Cloud Signature Consortium on 24 March 2026, where members came together to explore the implications of the EU Mercosur Free Trade Agreement and to connect with organisations newly joining the CSC community.
A Shift in Perspective: Trade Depends on Trust
While the EU Mercosur agreement is often discussed in terms of tariffs, goods, and market access, the session invited participants to look at it from a different angle.
Guest speaker Jean Everson Martina, Associate Professor at the Federal University of Santa Catarina (Brazil), highlighted that behind every cross border transaction lies a more fundamental question. Can we trust the data, the documents, and the identities involved?
What are often described as non tariff barriers, such as compliance checks, certifications, and validation processes, are in reality trust challenges. They determine whether transactions can move efficiently across borders or become delayed, duplicated, and costly.
As trade becomes increasingly digital, these challenges become more visible. Verifying origin, ensuring integrity, and achieving legal recognition across jurisdictions are no longer optional. They are essential infrastructure for global trade.
From Insight to Action: Trust Without Borders
Building on this discussion, Daniel Rendon, CSC Board Member from SSL.com, and the Regional Partner of the Trust Without Borders Summit 2026, highlighted how these themes will be taken forward at the upcoming event.
Taking place in Bogotá, Colombia, on May 13th-14th, the CSC Summit will bring together regulators, industry leaders, and technical experts from across regions to address the very challenges discussed during the session. The focus will be on aligning regulatory frameworks and technical standards, strengthening interoperability, and enabling trusted cross border digital transactions at scale.
Members interested in continuing the conversation and engaging directly with this global ecosystem are encouraged to learn more about the Trust Without Borders Summit and explore the programme at www.cscsummit.com.
Different Starting Points, Shared Objective
The session also highlighted an important dynamic between regions.
In Europe, trust frameworks are typically developed through a regulation first approach. In many Latin American countries, large scale digital systems have already been implemented in practice, with standardisation evolving over time.
These different starting points can create complexity, but they also create opportunity. The EU Mercosur agreement is not only about connecting markets. It is about connecting trust frameworks and finding ways to make them interoperable.
Welcoming CSC’s New Members
The session also marked the introduction of several organisations newly joining CSC, reflecting the consortium’s continued global growth and diversity.
New members welcomed to CSC include:
These organisations bring expertise across digital identity, PKI, and trust services, contributing to CSC’s mission of enabling secure and interoperable digital transactions worldwide.
Continuing the Conversation
If one message stood out from the session, it was this. Digital trade will only scale if digital trust crosses borders.
CSC members are encouraged to continue the discussion through upcoming initiatives, working groups, and events.
A full recording of the session will be made available in the CSC Community member area for those who would like to revisit the discussion or share it with colleagues.
For questions, contact: info@cloudsignatureconsortium.org.
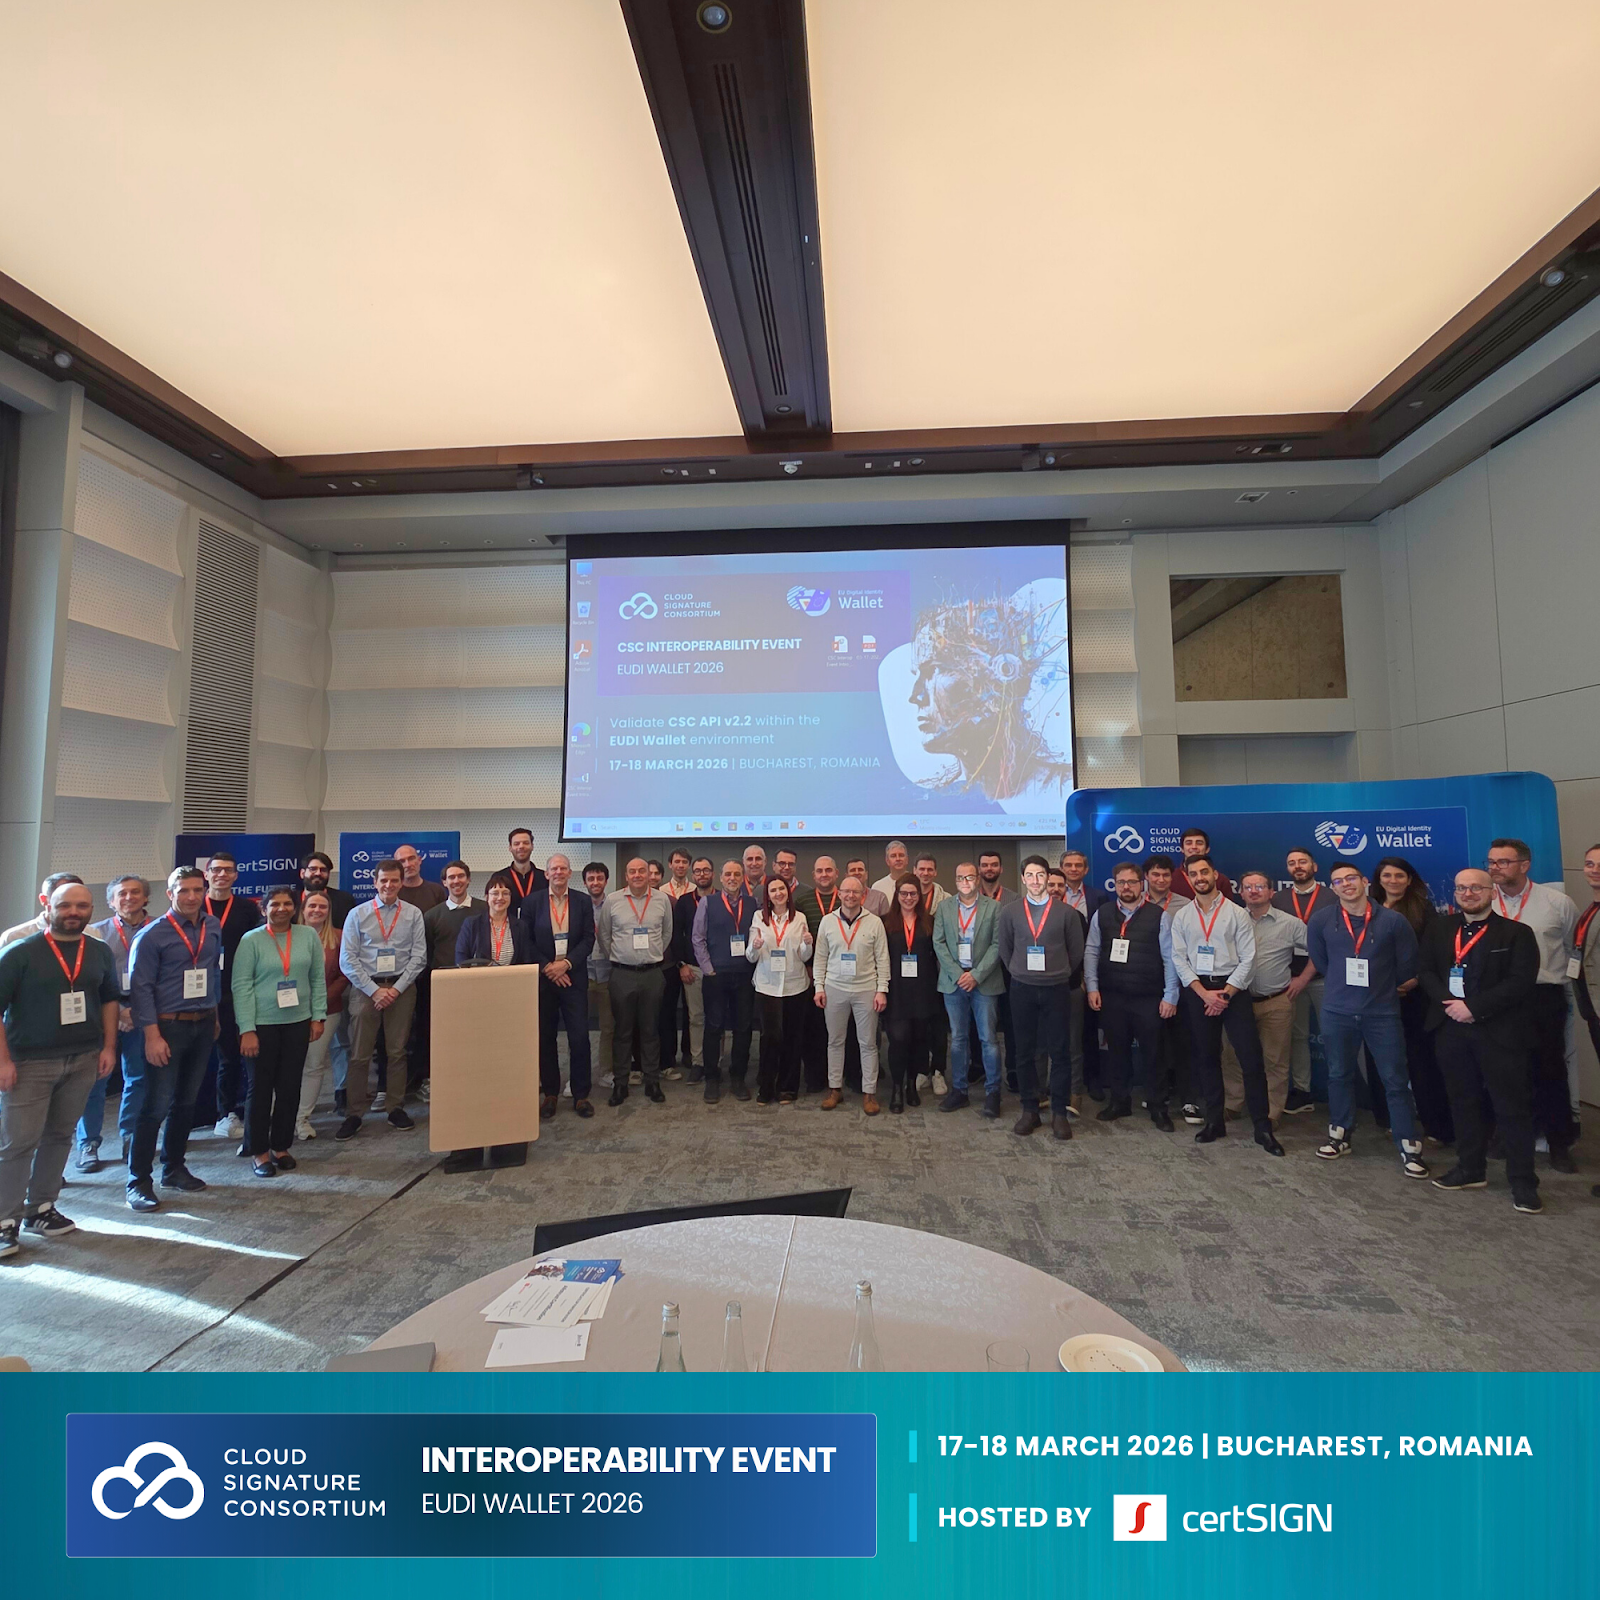
The Cloud Signature Consortium (CSC) successfully concluded its Interoperability Event 2026, held on 17–18 March in Bucharest and hosted by certSIGN. Bringing together EUDI Wallet providers, Qualified Trust Service Providers (QTSPs), and technology innovators from across Europe, the event marked an important step forward in advancing interoperability within the European Digital Identity ecosystem.
Over two days, participants moved beyond discussion to hands-on collaboration, testing real-world implementations of the CSC API within the EUDI Wallet framework. The programme combined strategic insights with deep technical engagement, covering remote signing use cases, API validation, and interoperability testing across multiple providers.
Day 1 focused on setting the context and technical groundwork, with sessions exploring the role of the CSC API in enabling secure, cross-border digital signatures. Participants then moved into environment setup and scenario planning, preparing for live testing.
Day 2 brought these efforts to life through live interoperability testing, cross-provider integrations, and real-world use case validation. Teams worked collaboratively to test, refine, and demonstrate their solutions, culminating in live demos and innovation showcases.
The event concluded with an awards ceremony recognising outstanding contributions. Intesi Group was named the winner of the CSC Interoperability Event 2026, highlighting their strong performance and commitment to advancing the CSC API ecosystem.
The Interoperability Event once again demonstrated the value of bringing the ecosystem together in a practical, testing-driven environment. As the European Digital Identity Wallet moves closer to large-scale deployment, initiatives like this play a critical role in ensuring technical readiness, alignment, and trust across stakeholders.
CSC extends its sincere thanks to all participants and to certSIGN for hosting the event in Bucharest.
The conversation continues at the upcoming Trust Without Borders Summit 2026 in Bogotá, where the global digital trust community will further explore the future of identity, signatures, and cross-border interoperability. Visit www.cscsummit.com for more information.
CSC Interoperability Event 2026 — In Numbers
95 plugtest registrations
3 with warnings
5 failed
Cloud Signature Consortium VZW
Rue du Luxembourg 22-24 | BE-1000 Brussels
ID BE0687.882.032
Privacy PolicyCopyright © 2026 CSC - Developed by ALYS